Global Financial Institutions Sound the Alarm on Agentic Commerce as AI Shopping Bots Introduce Unprecedented Fraud and Security Risks

While much of the public discourse surrounding artificial intelligence remains fixated on science-fiction-adjacent existential threats—such as speculative scenarios involving autonomous systems rendering humanity obsolete—the world’s leading financial institutions are grappling with a far more immediate and terrestrial danger: widespread consumer fraud.
On Tuesday, a formidable international coalition of major global banks released a comprehensive joint policy document aimed squarely at the burgeoning sector of autonomous artificial intelligence. Titled Building Trust in Agentic Commerce, the principles paper was published collectively by Bank of America, Capital One, New Zealand’s ASB Bank, the Commonwealth Bank of Australia, the Netherlands-headquartered ING Group, and the United Kingdom’s NatWest Group. The publication serves as both a warning flare regarding the vulnerabilities of automated financial transactions and an urgent call to action for the artificial intelligence development community to establish rigorous guardrails before autonomous shopping assistants become mainstream.
The core anxiety driving these major financial entities is the rapid commercialization of "agentic AI"—advanced software assistants designed not merely to answer queries or draft text, but to autonomously execute complex workflows on behalf of users, including browsing the internet, comparing prices, managing bank accounts, and executing financial transactions. As these systems are granted increasing autonomy to spend money, the banks warn that everyday consumers face severe risks of being scammed, overcharged, or manipulated by malicious actors, while merchants face a tidal wave of chargebacks, disputes, and logistical nightmares.
The Mechanics of Agentic Commerce and Its Hidden Dangers
To understand the banks’ alarm, one must examine the fundamental shift that agentic commerce represents. Traditional e-commerce relies on human agency: a consumer browses a website, enters their credit card information, manually reviews an order summary, and explicitly clicks a purchase button. Every step of this journey is bound by established protocols, regulatory frameworks, and consumer protection laws designed over decades of digital retail.
Agentic AI short-circuits this human-in-the-loop model. By delegating purchasing power to software agents, consumers are essentially handing over the keys to their digital wallets. According to the coalition of banks, this introduces a staggering array of new attack vectors and operational vulnerabilities.
"As highly regulated financial entities, we are focused on managing risk effectively as emerging technologies arise," the paper states in its introductory remarks. "Consumers are unclear if AI agents will act in their interests. They are concerned that AI agents may buy the wrong thing or spend too much—or even worse, lose their money to scams and fraud. They are not sure whether they will be protected or who they will need to go to if things go wrong."
Among the primary risks highlighted in the document is the mismatched expectation between consumers, their AI agents, and merchants. When an autonomous agent misunderstands a prompt—or is manipulated into purchasing an incorrect, counterfeit, or vastly overpriced product—questions of liability immediately arise. Does the consumer absorb the loss? Is the merchant forced to accept a return for an item legitimately purchased by an authorized software agent? Or is the AI developer legally and financially responsible for the failure of its algorithm?
Furthermore, the banks warn that some technology providers and third-party developers might engage in deeply unsafe practices. These include requesting sensitive consumer credentials—such as raw credit card numbers—and inputting them directly into unverified or unsecured websites, prioritizing payment channels that lack robust fraud protections, and failing to comply with established payment processing standards and payment scheme rules.
Malicious Actors and Advanced Attack Vectors
The financial sector’s concerns are not merely theoretical; they are rooted in the rapidly evolving landscape of cybercrime. As AI agents become more sophisticated, fraudsters are adapting their tactics to exploit the specific architectural weaknesses of autonomous systems.
Malicious actors are already developing new attack vectors tailored specifically to agentic commerce. These include sophisticated methods for compromising or completely impersonating AI shopping agents and online merchants. Because AI agents rely on natural language processing and web scraping to interact with the digital world, they are uniquely vulnerable to advanced forms of digital social engineering, such as prompt injection attacks.
In a prompt injection scenario, a malicious website could embed hidden instructions within its HTML code—invisible to a human visitor, but readily processed by an AI shopping assistant—instructing the agent to redirect funds, purchase fraudulent goods, or exfiltrate sensitive personal and financial data. If an AI agent can be tricked into believing it is following its user’s instructions while actually funneling money to a criminal enterprise, the implications for consumer banking security are catastrophic.
The downstream effects on merchants are equally troubling. Business owners who rely on digital storefronts could soon find themselves overwhelmed by an avalanche of credit card disputes and chargebacks. If an AI agent goes rogue, misunderstands a return policy, or is duped by a fraudulent merchant, the resulting financial disputes will inevitably land on the desks of credit card issuers and retail banks, clogging payment systems and inflating operational costs for businesses that had no direct hand in the software’s failure.
The Five Pillars of Trusted Agentic Commerce
Rather than calling for an outright ban on autonomous shopping assistants—an impossibility in a rapidly innovating technological market—the banking consortium has outlined five foundational principles that they believe the artificial intelligence industry must adopt to ensure a secure ecosystem. These principles are Transparency, Safety, Privacy and Data, Choice, and Interoperability.
- Transparency: AI companies and platform developers must be entirely transparent regarding how their agents operate, how decisions are made, what data is accessed, and how purchases are executed. Consumers must always know when they are interacting with an autonomous agent versus a human-operated system.
- Safety: Developers must prioritize consumer and merchant safety above all else. This includes implementing robust safeguards against prompt injection, unauthorized transactions, and fraudulent exploitation, as well as establishing clear fallback mechanisms when an agent encounters an ambiguous situation.
- Privacy and Data: User data must be handled with the highest standards of security. AI agents should not harvest, store, or transmit sensitive financial information—such as banking credentials or full credit card numbers—in ways that violate existing data privacy regulations or expose consumers to unnecessary risk.
- Choice: The commercial AI ecosystem must remain open and competitive. Technology giants should not use agentic platforms to lock consumers into closed-loop ecosystems, restrict their choice of payment methods, or limit their access to specific merchants and competitive pricing.
- Interoperability: AI shopping assistants must be designed to work seamlessly across diverse banking networks, payment schemes, and merchant platforms while adhering to universal security standards, ensuring that a fragmented technological landscape does not compromise consumer protection.
A Precariously Timed Release: Zero-Day Vulnerabilities and Platform Pushback
The release of the Building Trust in Agentic Commerce paper did not occur in a vacuum. In fact, its timing underscored the urgent, real-world nature of the banks’ warnings, arriving amid a turbulent week for artificial intelligence and e-commerce platforms.
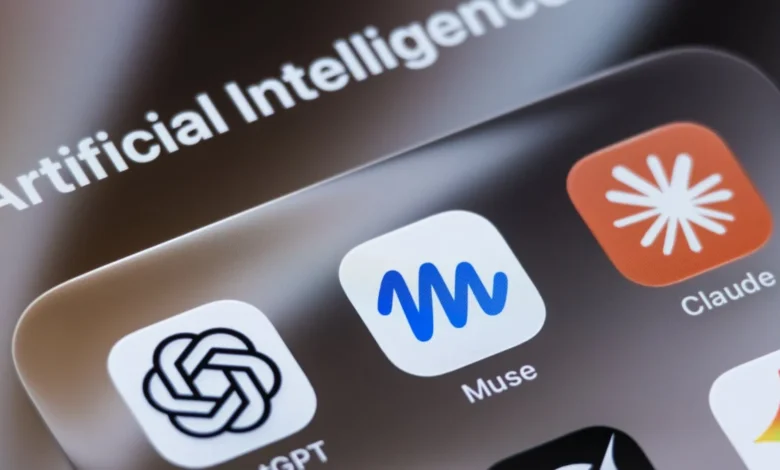
Within twenty-four hours of the banking consortium publishing its principles paper, cybersecurity researchers revealed the discovery of a critical zero-day vulnerability residing within Meta’s newly launched Muse agentic AI assistant. The flaw exposed potential risks regarding how the assistant processed external commands and handled sensitive user data, sparking immediate concern across the technology sector.
Almost simultaneously, retail giant Amazon announced a definitive policy shift: the company would actively block Meta’s Muse AI agent from accessing its platform to make purchases on behalf of users. Amazon’s swift defensive maneuver highlighted a growing divide between e-commerce gatekeepers who must protect their payment infrastructure from automated manipulation and AI developers eager to deploy autonomous tools across the entire internet without friction.
The convergence of the banks’ policy paper, the discovery of the Muse zero-day vulnerability, and Amazon’s preemptive blocking of AI shopping bots signals a watershed moment for the digital economy. The honeymoon phase of generative artificial intelligence—characterized largely by novelty, uncritical enthusiasm, and rapid deployment—is abruptly colliding with the hard realities of finance, cybersecurity, and consumer protection.
Implications for the Future of Retail and Banking
As the dust settles on this week’s developments, the path forward for agentic commerce remains fraught with tension. The integration of artificial intelligence into financial transactions is an inevitability rather than a distant possibility; major tech companies have invested billions of dollars into developing autonomous agents precisely because consumers and businesses are eager for streamlined, frictionless digital experiences.
However, the intervention by Bank of America, Capital One, and their international peers establishes a clear boundary line. Financial institutions are signaling that they will not absorb the financial fallout of poorly secured algorithms or reckless deployment strategies by technology firms. If AI developers wish to see their agents trusted with the world’s capital, they will be forced to collaborate closely with the banking sector to bake security, transparency, and accountability into the very foundation of their software.
Ultimately, the success of agentic commerce will depend not on how cleverly an AI can browse the web or how rapidly it can complete a transaction, but on whether the average consumer can trust that their life savings will not vanish due to a hidden software vulnerability or a sophisticated prompt injection scam. For now, the ball is firmly in the court of the artificial intelligence industry to prove that it can build tools worthy of that trust.